 Endpoint Index
Which Endpoint Security Vendors Sign a HIPAA BAA? (October 2026)
Only three of the 14 vendors we track say they will sign one, and two of the best-known managed services say outright that they will not.
Contents
Executive summary
Three of the 14 endpoint security vendors Endpoint Index tracks say they will sign a HIPAA business associate agreement for the products listed here: Trend Micro, SentinelOne and, for some configurations only, Acronis. Two of the best-known managed services for small businesses, Huntress and ThreatDown, say they will not, because their products are not meant to handle health information. The other nine publish no offer to sign one, so a practice using any of them has to ask in writing. Statuses were last checked on 2 October 2026.
For the buying decision, which product suits a practice and why, see the medical and dental practice guide. This page is the register behind it.
This is general information, not legal advice.
Which vendors sign a BAA?
| Vendor and products | Signs a BAA? | What the vendor says | Source |
|---|---|---|---|
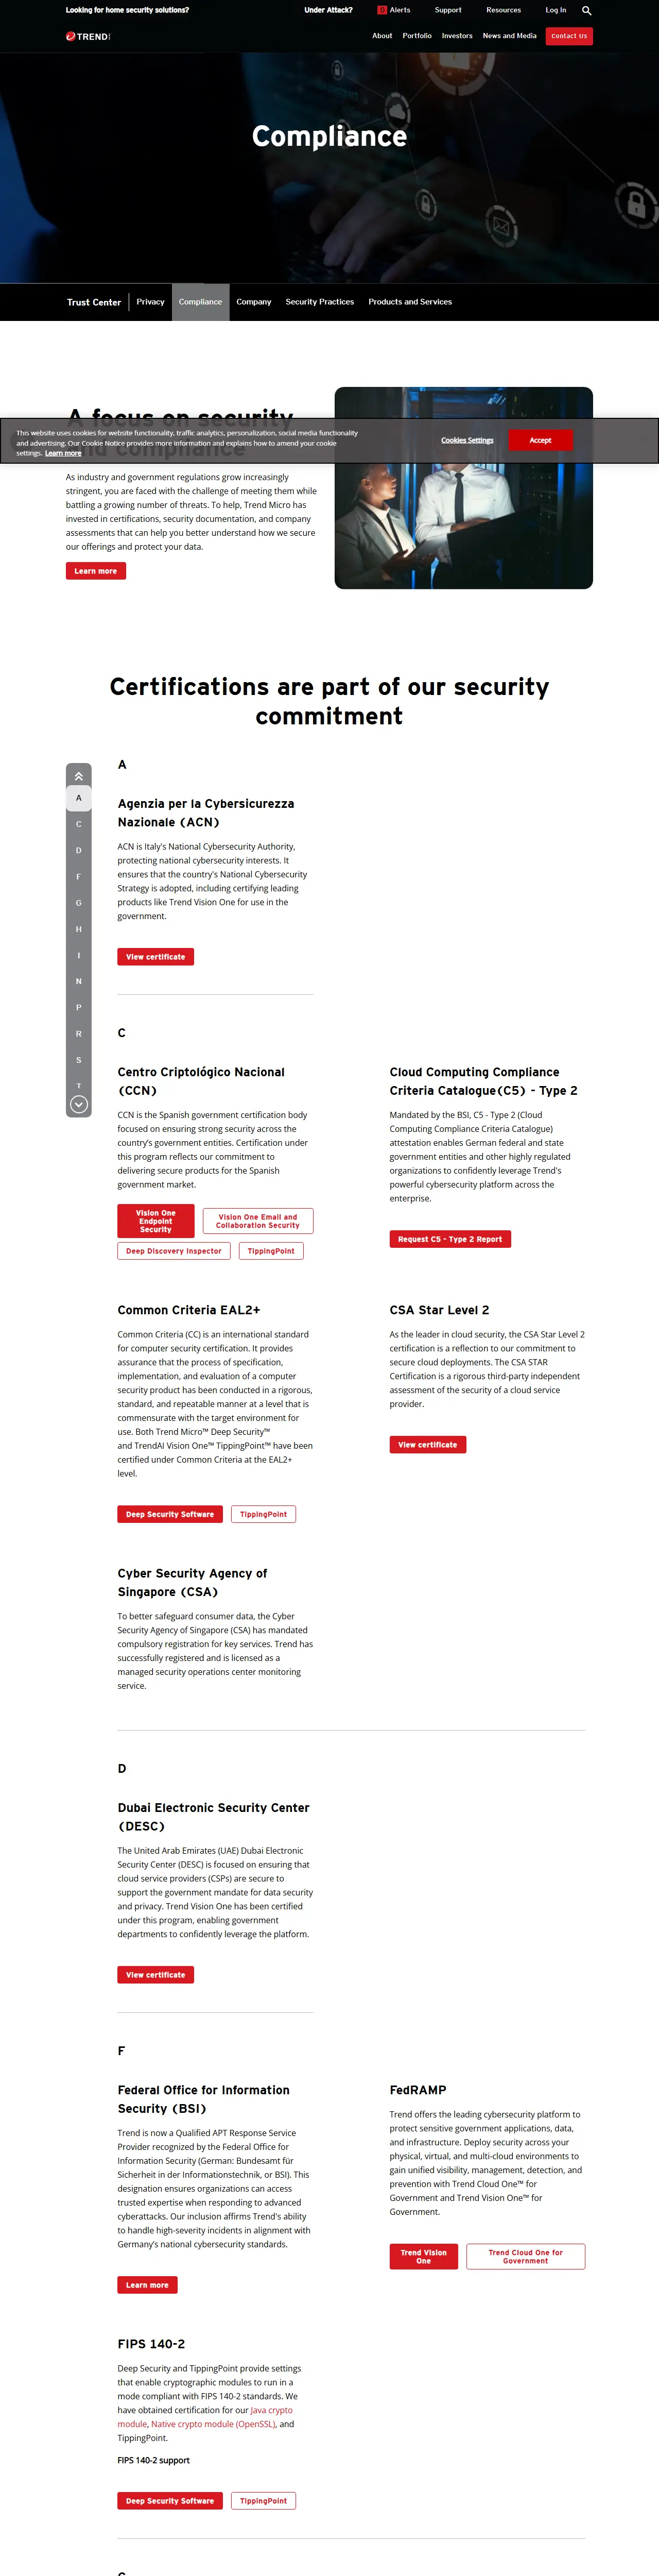
| Trend MicroTrend Micro Worry-Free Services Advanced | Yes | Publishes a HIPAA business associate agreement, an addendum to its Global Products Agreement, linked from its trust centre. HIPAA regulations require that covered entities enter into agreements with business associates to ensure that PHI is adequately protected. View Business Associate Agreement | trendmicro.com · screenshot |
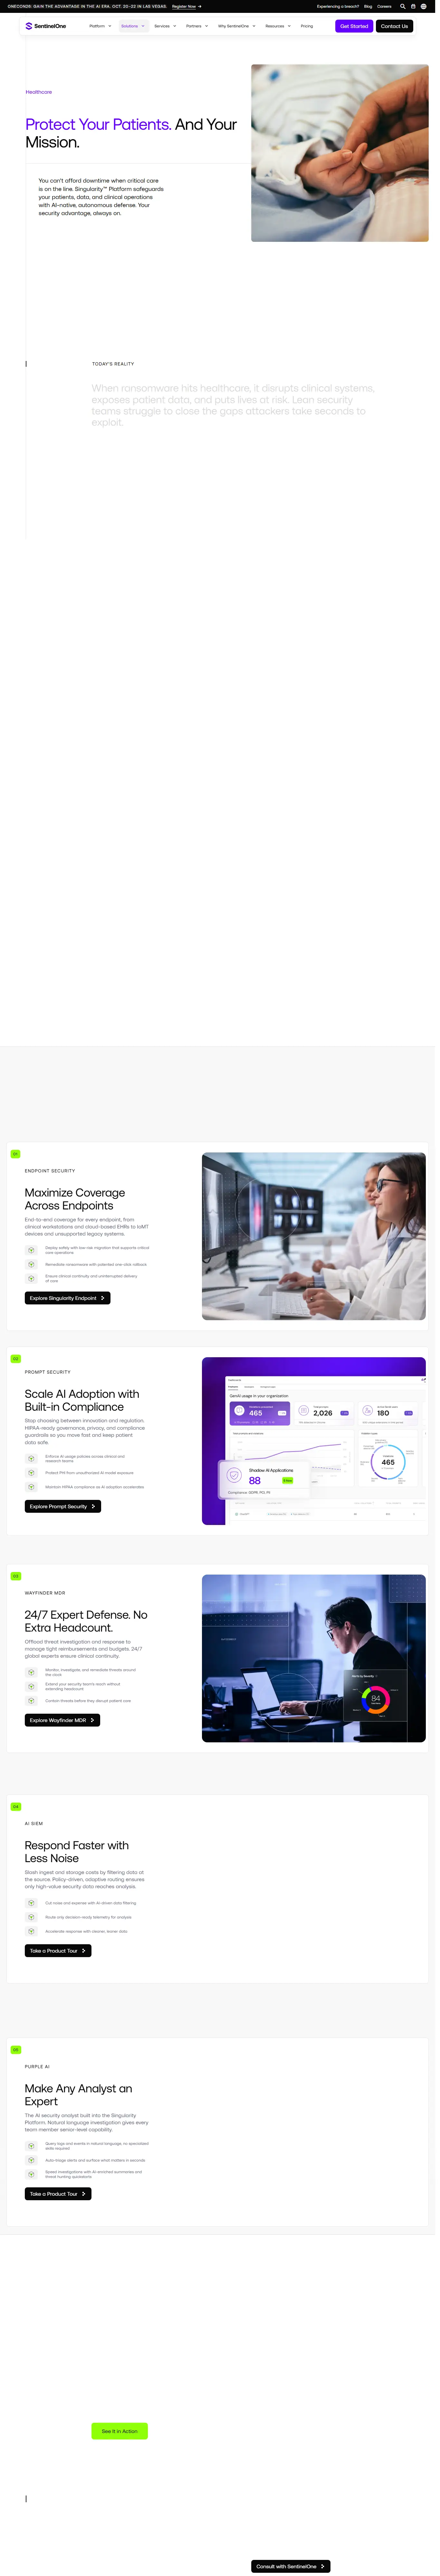
| SentinelOneSentinelOne Singularity ControlSentinelOne Singularity Complete | Yes | Says supporting a healthcare customer may include signing a BAA when it processes PHI on the customer's behalf. When SentinelOne processes PHI on behalf of a customer as a Business Associate, we are committed to helping support the customer's compliance requirements, which may include signing a Business Associate Agreement. | sentinelone.com · screenshot |
| AcronisAcronis Cyber Protect | Yes | Signs a BAA only for Cyber Protect Cloud, or Cyber Protect Advanced with Acronis Cloud Storage in a US data centre, on request through an account manager. a BAA cannot be signed in advance. | kb.acronis.com |
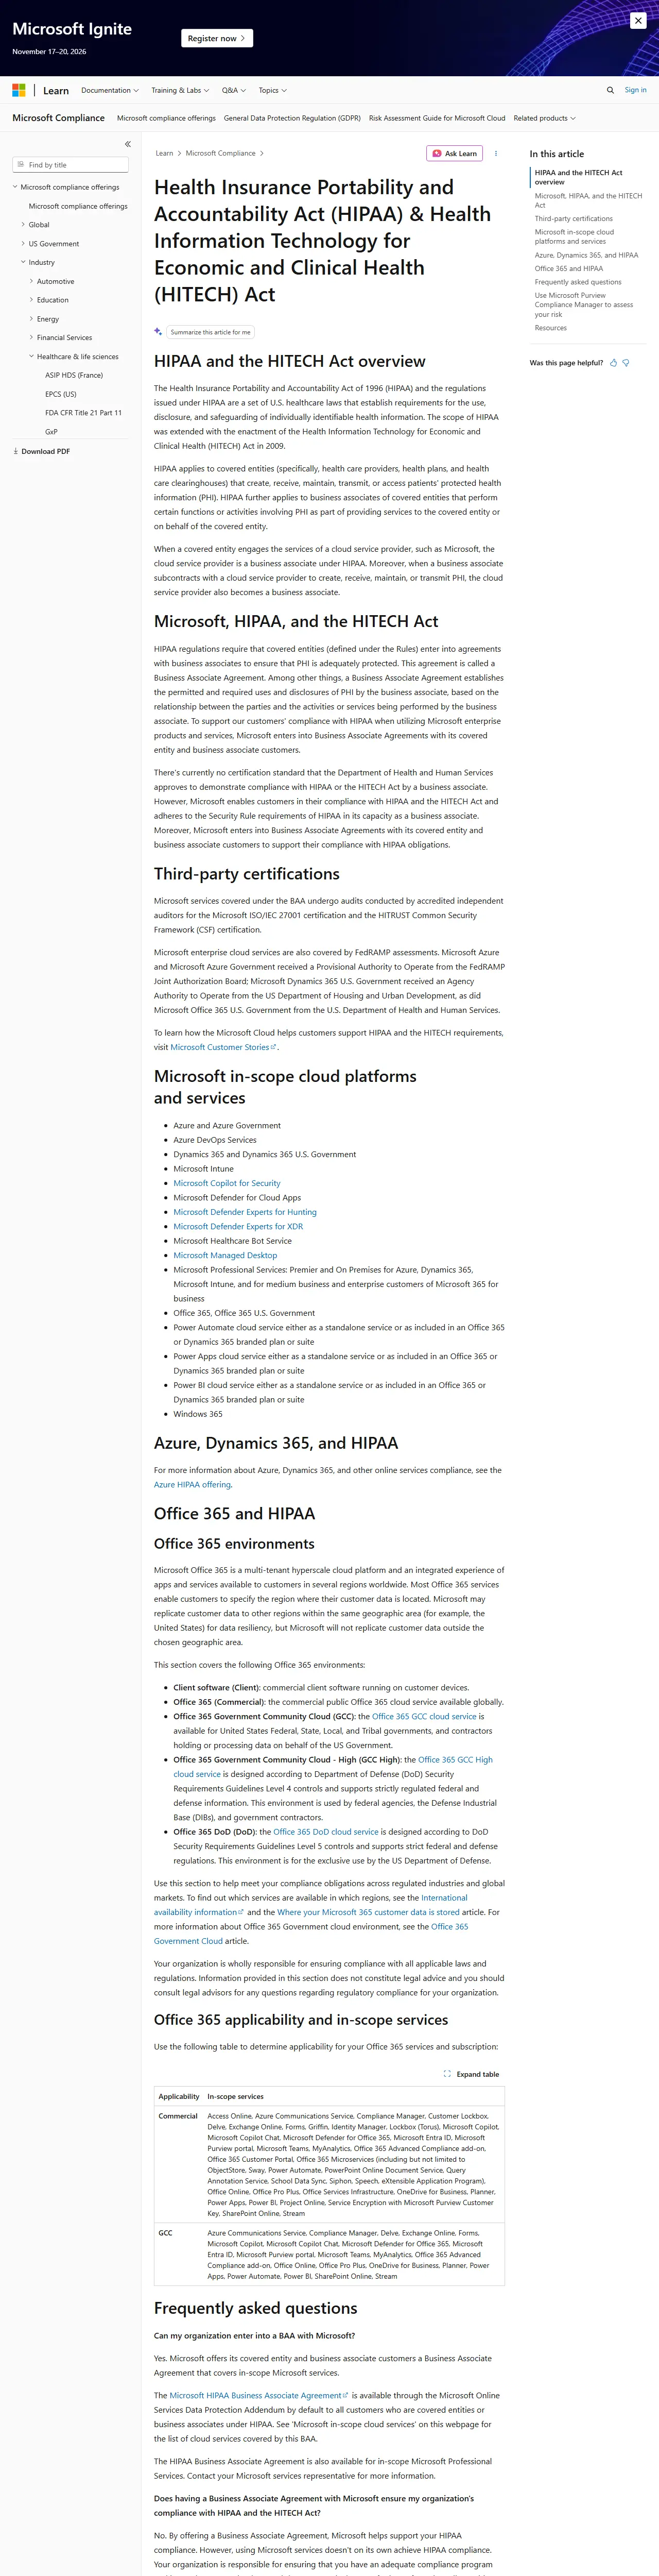
| MicrosoftMicrosoft Defender for Business | Not stated | Its BAA covers a published list of in-scope services; neither Defender for Business nor Defender for Endpoint was on that list. Microsoft offers its covered entity and business associate customers a Business Associate Agreement that covers in-scope Microsoft services | learn.microsoft.com · screenshot |
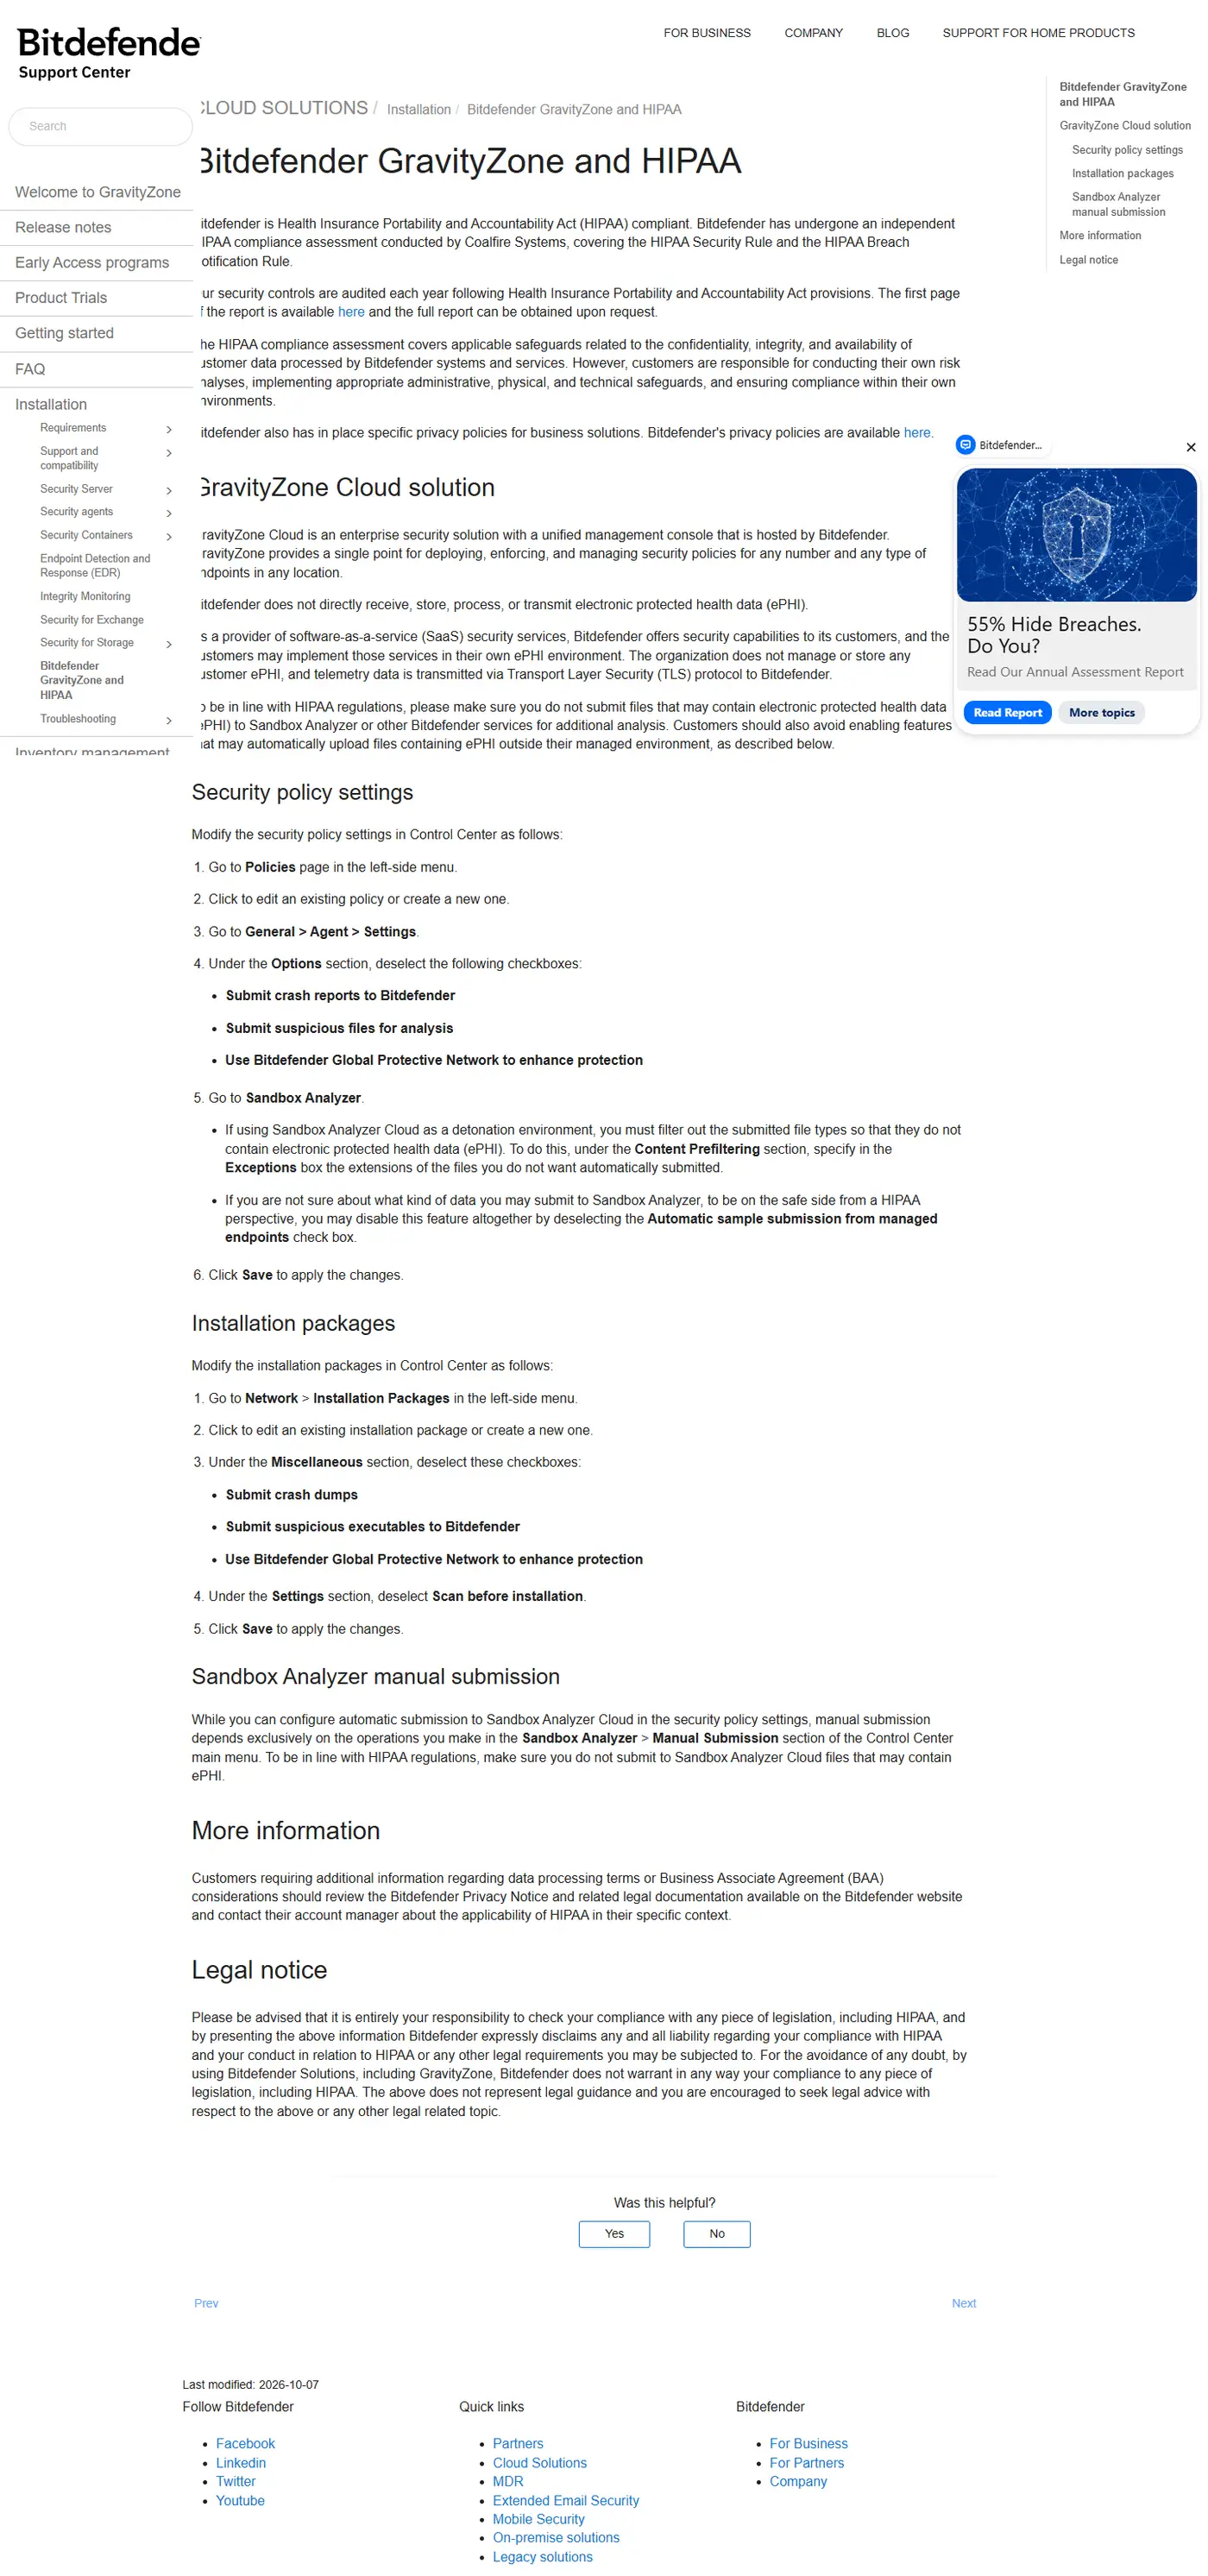
| BitdefenderBitdefender GravityZone Business SecurityBitdefender GravityZone Business Security Premium | Not stated | Reports an independent HIPAA assessment and sends BAA questions to the customer's account manager; does not say it signs one. Customers requiring additional information regarding data processing terms or Business Associate Agreement (BAA) considerations should review the Bitdefender Privacy Notice and related legal documentation available on the Bitdefender website and contact their account manager about the applicability of HIPAA in their specific context. | bitdefender.com · screenshot |
| CrowdStrikeCrowdStrike Falcon Go | Not stated | Publishes a third-party HIPAA report for the Falcon platform; no CrowdStrike page we found mentions a BAA. the Falcon platform was verified as addressing eight key Health Insurance Portability and Accountability Act (HIPAA) technical requirements | crowdstrike.com · screenshot |
| SophosSophos Endpoint | Not stated | Lists a HIPAA attestation for Sophos Central products, with the report on request; no Sophos page we found mentions a BAA. All Sophos Central products ... carry a 2020 SOC2 Type 1 and HIPAA Type 1 attestation. | sophos.com · screenshot |
| CynetCynet All-in-One | Not stated | Maps its reporting to HIPAA; no Cynet page we checked (compliance hub, trust page, EULA) says it signs a BAA. Cynet maps directly to the compliance frameworks your customers live by, from NIST to HIPAA to DORA | cynet.com · screenshot |
| ESETESET PROTECT Core | Not stated | Markets HIPAA as a regulation its products help with; its trust centre lists no HIPAA attestation and no BAA. Explore the regulations that ESET solutions can help you comply with | eset.com · screenshot |
| WatchGuardWatchGuard Endpoint Security 360 | Not stated | Its HIPAA page describes how its products support HIPAA safeguards, but neither offers nor rules out a BAA. | watchguard.com |
| WebrootWebroot Business Endpoint Protection | Not stated | No HIPAA statement for this product; its parent OpenText's compliance pages cover other services. | webroot.com |
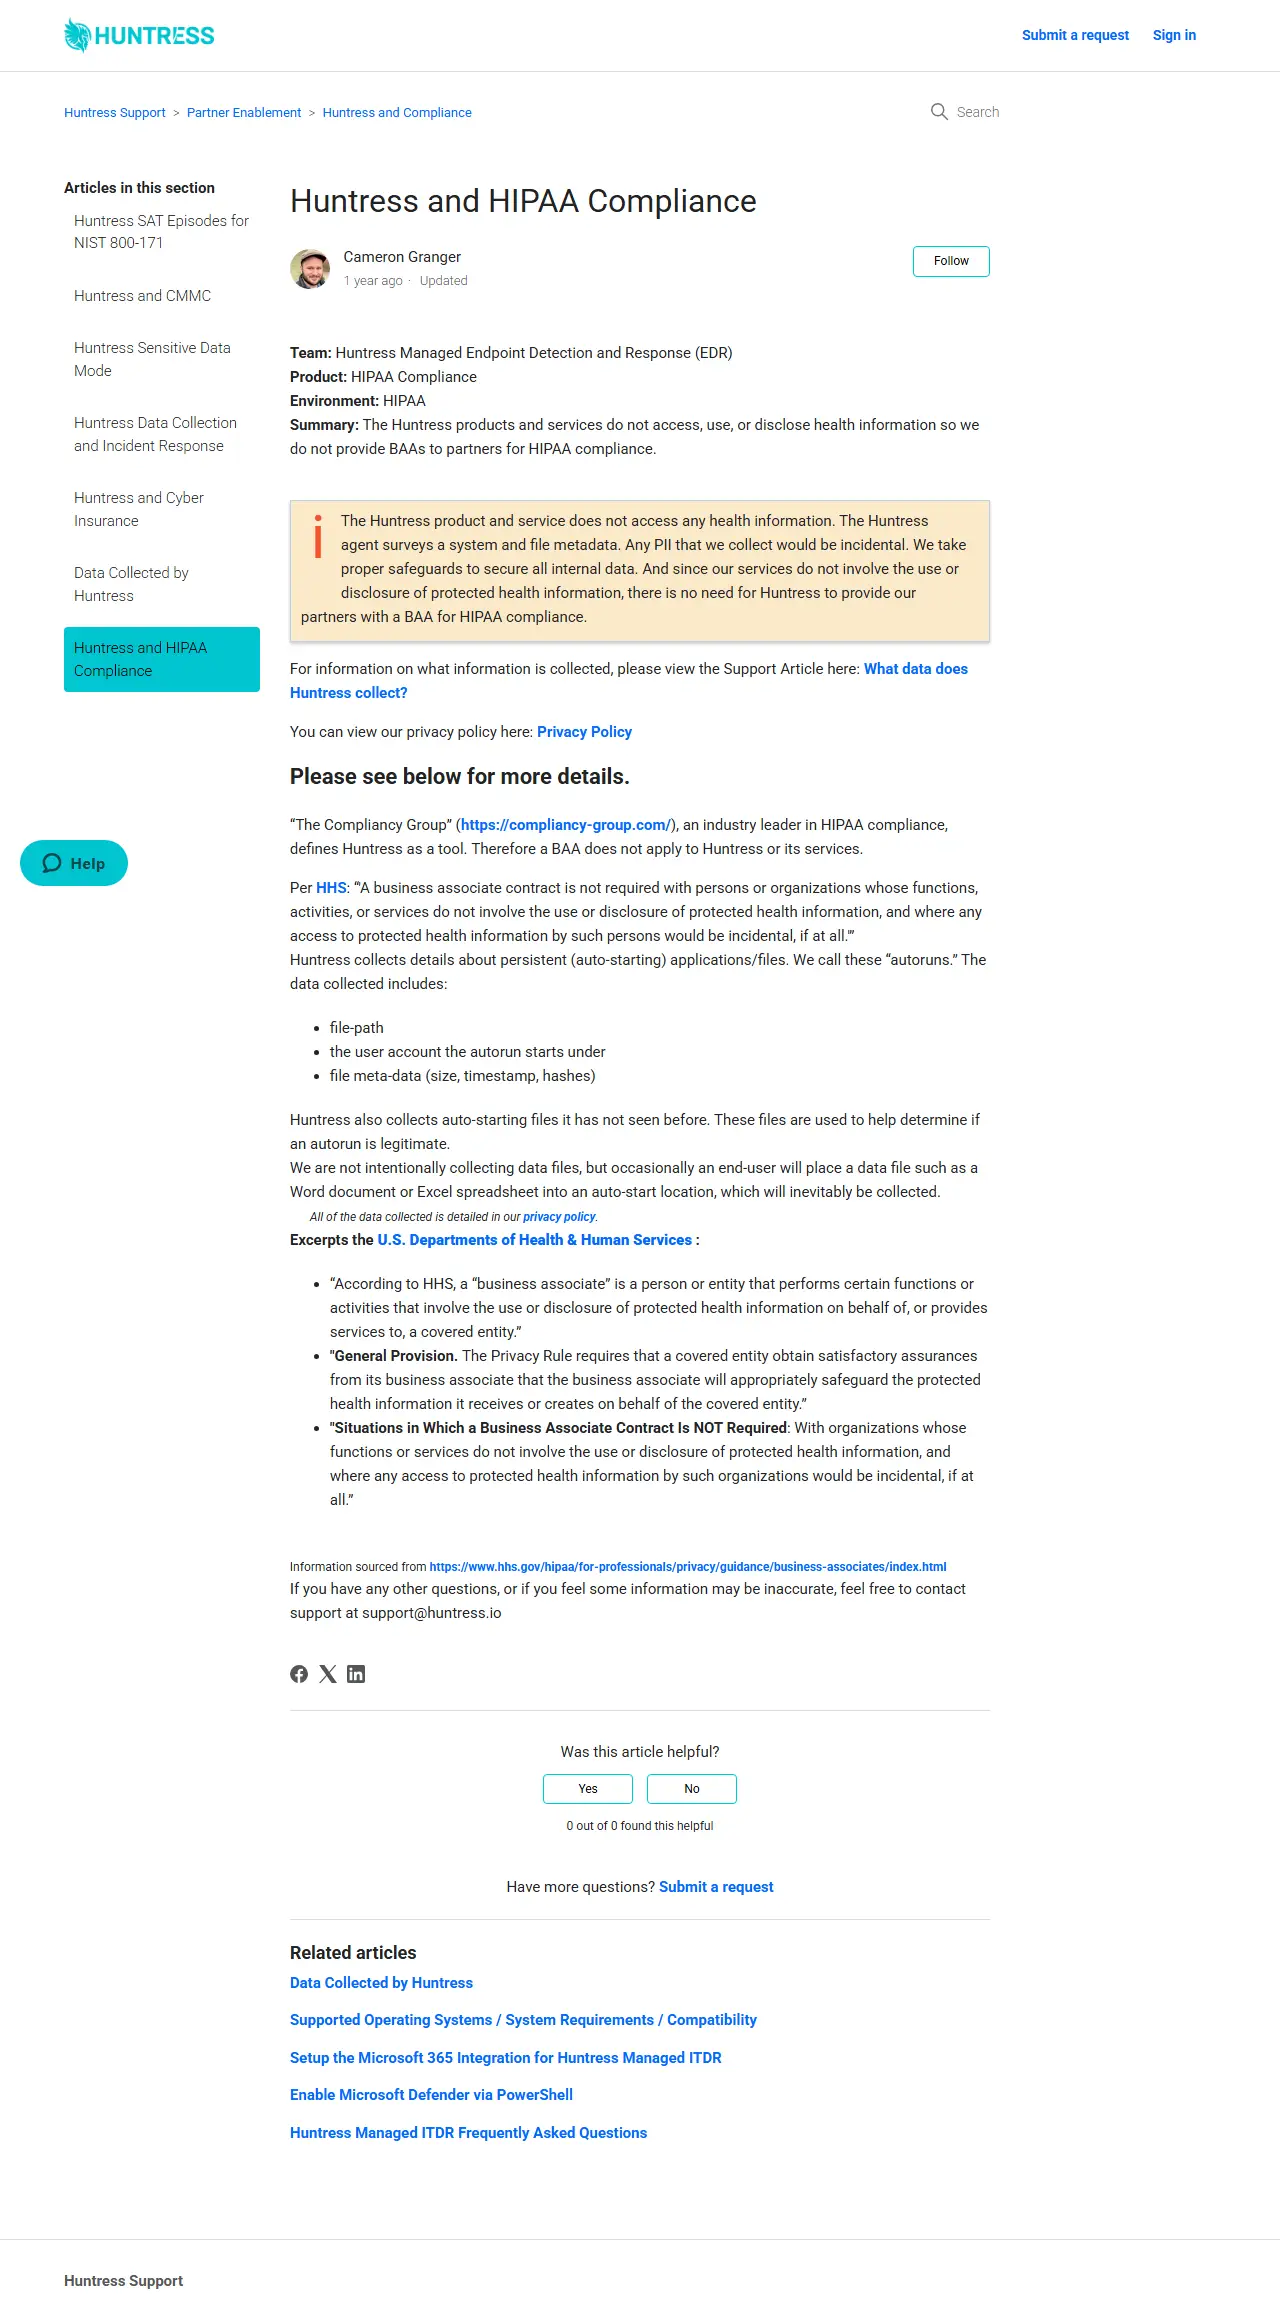
| HuntressHuntress Managed EDR | No | Does not provide BAAs, on the grounds that its products do not touch health information. The Huntress products and services do not access, use, or disclose health information so we do not provide BAAs to partners for HIPAA compliance. | support.huntress.io · screenshot |
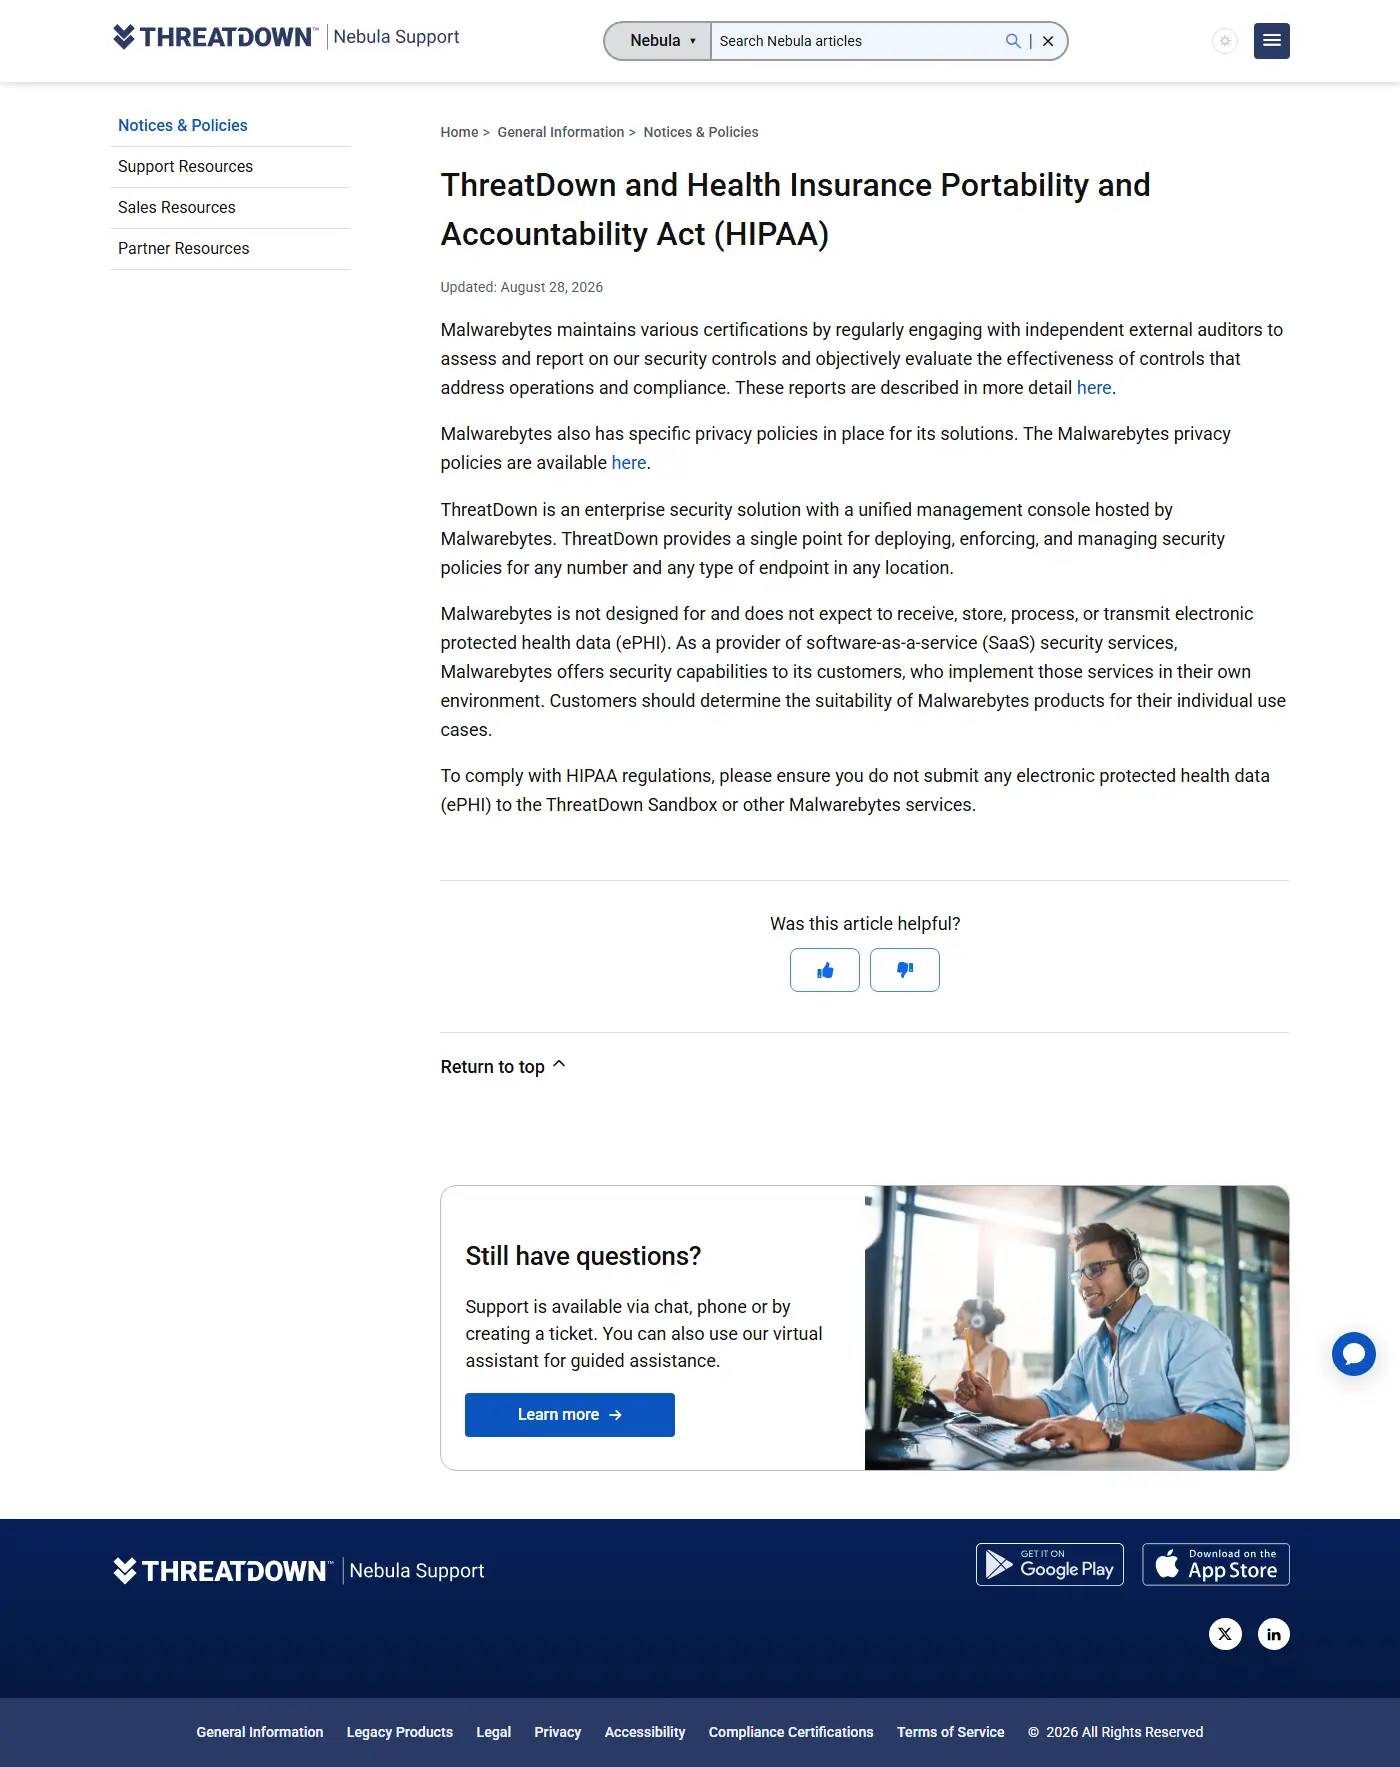
| ThreatDownThreatDown AdvancedThreatDown Elite | No | Says its products are not designed to receive health data, and asks customers not to send any to its sandbox. Malwarebytes is not designed for and does not expect to receive, store, process, or transmit electronic protected health data (ePHI). | support.threatdown.com · screenshot |
| AvastAvast Ultimate Business Security | No | No HIPAA or BAA statement on any Avast Business product or subscription page we checked. | avast.com |
Why do some vendors refuse to sign?
A business associate, under HIPAA, is a vendor that creates, receives, maintains or transmits protected health information on a covered entity's behalf. Huntress and ThreatDown both argue they are not one: Huntress says its products "do not access, use, or disclose health information", and ThreatDown says its software is "not designed for and does not expect to receive" health data. Bitdefender takes a softer line, saying it does not directly receive health data, and leaves BAA questions to the account manager.
Whether that holds for your practice depends on how the product is set up. Endpoint agents can upload suspicious files for analysis, and a file can contain patient records. ThreatDown and Bitdefender both tell healthcare customers not to send files with health data to their sandboxes. If you keep a product whose vendor will not sign, switch automatic file submission off and record that you did.
What should a practice do if its vendor will not sign?
- Ask in writing. A vendor whose site is silent may still sign on request; Acronis, for one, says a BAA "cannot be signed in advance" and is arranged through an account manager.
- Get the refusal in writing too, with the vendor's reasoning, and give it to whoever advises you on HIPAA.
- Turn off automatic sample submission to cloud sandboxes, as Bitdefender and ThreatDown advise.
- Prefer a vendor that publishes a BAA when you are choosing from scratch. The medical and dental guide ranks the options with that in mind.
Frequently asked questions
Does Huntress sign a HIPAA BAA?
No. Huntress says its products "do not access, use, or disclose health information so we do not provide BAAs to partners for HIPAA compliance."
Does Microsoft's BAA cover Defender for Business?
Not on Microsoft's published list. Its BAA covers "in-scope Microsoft services", and neither Defender for Business nor Defender for Endpoint appeared on that list when we checked. Ask Microsoft before relying on it.
Does SentinelOne or ThreatDown sign a BAA?
SentinelOne does, on request: its healthcare page lists signing a BAA among the things it "may include". ThreatDown does not sign one: it says its products are not designed to receive health data.
Is a HIPAA attestation the same as a BAA?
No. An attestation, like Sophos's or Bitdefender's HIPAA assessment, says an auditor reviewed the vendor's own safeguards. A BAA is a contract in which the vendor takes on obligations for your patients' data. A practice that needs the second is not covered by the first.
Methodology and caveats
Each status reflects what the vendor's own pages said when we checked, recorded on the product page with its source and date; "Not stated" means we found no statement either way, not that the vendor refuses. Statements cover the products listed, not every product the vendor sells. Vendors change their positions, so confirm in writing before you sign. This is not legal advice.
Sources
- U.S. Department of Health and Human Services, Business associates: who counts as a business associate.
- Each vendor's statement, linked in the register above, with a dated screenshot where we hold one.
- Endpoint Index product pages for each product listed, with the regulatory fields and their verification dates.
Related research
All research ›Methodology · Report an error · Vendor not listed? Get listed